
















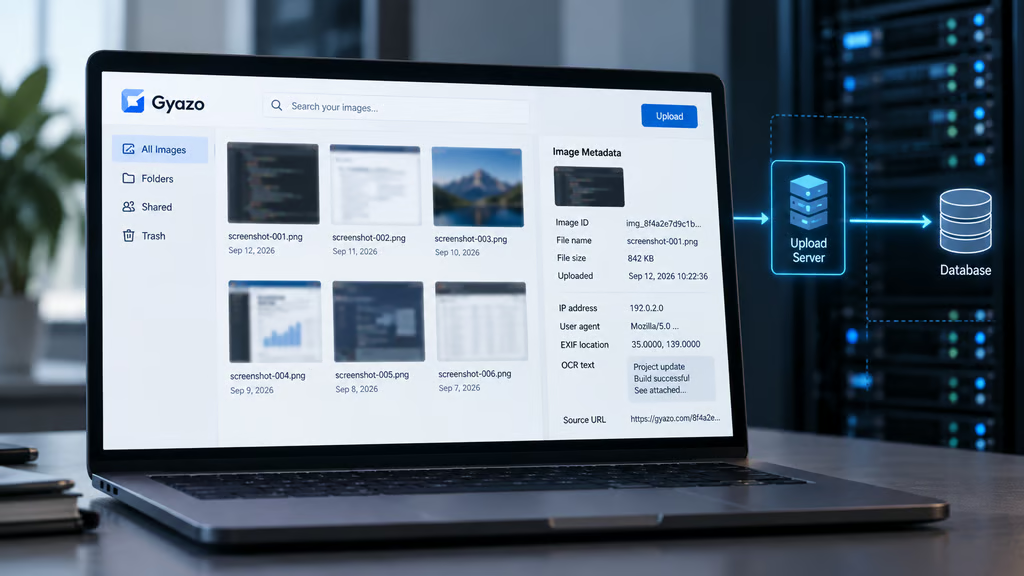


A screenshot can reveal much more than what appears on the screen. API keys, terminal output, internal dashboards, location data, and sensitive text can all end up inside an image or its metadata.
Image-sharing service Gyazo said a breach exposed about 23.62 million user records and 490 million image metadata records after an attacker compromised an image upload server. The affected account data included email addresses and password hashes, while the metadata varied by record and could include IP addresses, EXIF location information, OCR-extracted text, image IDs, and source URLs.
For defenders, some of that metadata may create risks that last much longer than a password reset.
Attacker moved from an upload server to Gyazo’s database
According to The Hacker News, the attacker exploited an unspecified vulnerability in Gyazo’s image upload server and gained the ability to execute arbitrary commands on the affected server.
Helpfeel, which operates Gyazo, detected suspicious activity on Sept. 11. By early Sept. 12, the company said it had blocked the identified access routes, terminated the attacker’s connections, and fixed the vulnerability. It confirmed that data had been exposed on Sept. 14, notified Japan’s Personal Information Protection Commission on Sept. 15, and publicly disclosed the breach on Sept. 16.
Affected user records could contain names, email addresses, password hashes, user and device IDs, login session IDs, X integration tokens, Google SSO email addresses, profile details, and account activity. Helpfeel said payment card information was not exposed.
The 23.62 million figure refers to records, not necessarily 23.62 million individual victims. Anonymous accounts are also included, and Helpfeel is still determining how many people had personal information exposed.
490M metadata records include locations, OCR text, and image IDs
The much larger metadata exposure may be harder to address than compromised account credentials.
Most of the 490 million records are tied to images registered in January 2019 or earlier. The exposed metadata could reveal several different types of information:
- Where an image came from: Upload IP addresses and EXIF coordinates can provide clues about a user’s location.
- What appeared in a screenshot: OCR data can contain extracted text, while titles and source URLs may provide additional context.
- How an image can be reached: Image IDs are used to construct Gyazo URLs, while some records also included hashed passphrases for private images.
Gyazo normally uses a 32-character image ID as part of each capture’s URL. The long identifier is designed to make an unshared link difficult to guess. Once image IDs are exposed, however, the URLs may no longer provide the same protection against unauthorized discovery, particularly for captures that did not require additional access controls.
Helpfeel temporarily disabled viewing for some images and said it cannot rule out the possibility that the attacker viewed some private captures.
The risk can be particularly serious for developers and businesses that used Gyazo to share work screenshots. Infosecurity Magazine noted that screenshots may contain terminal output, API keys, configuration files, credentials, internal applications, and sensitive documents.
Gyazo’s OCR feature adds another problem because text inside a screenshot can be extracted and stored as searchable data rather than remaining visible only in the image.
“The metadata layer is where the real reach is,” Seemant Sehgal, founder and CEO of BreachLock, told eSecurity Planet.
Sehgal pointed to EXIF coordinates, OCR text, session IDs, and image URL information as data that could help an attacker piece together user activity and location history.
The age of much of the data provides some relief. API keys and other credentials exposed in screenshots from 2019 or earlier may already have expired or been rotated. Location information, internal URLs, personal details, and long-lived credentials can remain useful much longer.
Gyazo breach puts internal segmentation in focus
The upload-server vulnerability explains how the attacker got in. The scale of the exposure raises another security issue: how much a compromised internet-facing system was able to access after the initial intrusion.
Sehgal said allowing arbitrary command execution on an image upload server was a serious security failure, but the proximity of that server to a database containing hundreds of millions of records points to weak internal segmentation.
COE Security similarly warned that a vulnerable application component becomes far more dangerous when it has excessive privileges or unrestricted access to backend resources.
Security teams can reduce the blast radius by focusing on three controls:
- Limit privileges: Internet-facing applications should receive only the database and system permissions they need.
- Segment sensitive systems: Upload servers, databases, storage, and administrative environments should be separated where practical.
- Watch for unusual access: Command execution, abnormal database queries, and unexpected administrative activity should trigger investigation.
COE Security also recommends secure file-processing controls, continuous monitoring, and vulnerability management for internet-facing applications.
Patching the upload server only fixes the entry point. Security teams also need to limit what internet-facing systems can access, so compromising one service does not give an attacker a path to large stores of sensitive data.
What Gyazo users and security teams should do now
Helpfeel has asked all Gyazo users to change their passwords and update credentials on other services where the same or similar passwords were used. Users should also watch for suspicious emails or messages that use information from the breach to impersonate Gyazo or another trusted service.
Organizations whose employees used Gyazo for development or internal collaboration should consider reviewing older screenshots for credentials and secrets that may still be valid.
Security teams should prioritize:
- Rotating exposed secrets: Replace API keys, tokens, passwords, and other credentials that may still be active.
- Invalidating sessions and integrations: Review exposed session IDs and third-party tokens rather than focusing only on passwords.
- Monitoring follow-on attacks: Watch for credential stuffing, suspicious logins, phishing, account takeover attempts, and fake breach notifications.
Organizations should not assume older screenshots are harmless. They should identify any captures containing credentials, internal URLs, customer information, or location data and verify that exposed secrets, sessions, and integrations have been invalidated.
The Gyazo breach shows why incident response must extend beyond password resets. Credentials can be replaced, but location histories, indexed screenshot text, and internal information captured years ago may be impossible to retrieve once exposed.
Read more: Gyazo is not the only recent case where weak access controls opened the door to sensitive data, with researchers also finding 220.8 million passenger and crew records exposed through default credentials.