

















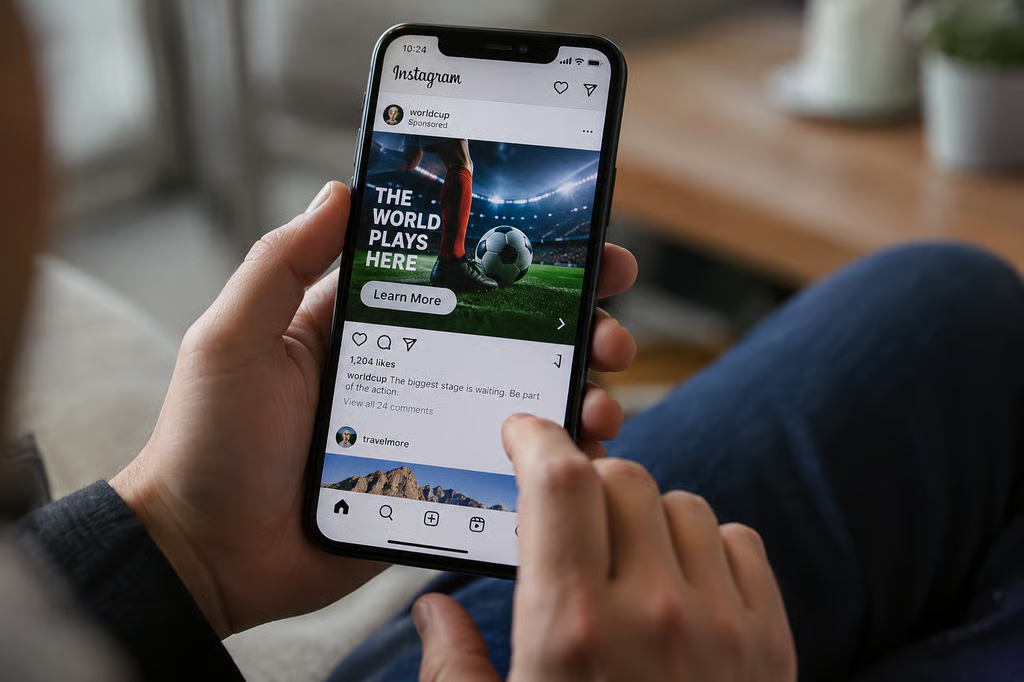
An iPhone user reportedly became infected with spyware simply by scrolling past an Instagram advertisement, without clicking anything.
Researchers at mobile security firm iVerify and website security company Report URI have documented campaigns that abuse the infrastructure behind ordinary web browsing to target vulnerable iPhones.
In one case reported by Axios, a financial institution employee's iPhone was infected after the employee scrolled past a soccer advertisement on Instagram without reportedly clicking it. The incident highlights a troubling reality: sophisticated spyware attacks can sometimes succeed without victims clicking suspicious links or downloading malicious files.
How the spyware attacks work
The research describes two distinct attack methods: DeadTag's abuse of expired website domains and a separate incident involving a malicious Instagram advertisement.
DeadTag, investigated by Report URI, involves attackers buying expired domains that legitimate websites still reference for third-party scripts, such as analytics tools. By taking control of these domains, attackers can serve malicious code to visitors.
Researchers linked the operation to exploit kits including Coruna and DarkSword, which combine multiple vulnerabilities to compromise susceptible iOS devices. Successful exploitation can allow attackers to bypass security protections and deploy spyware capable of accessing sensitive information, including stored credentials and cryptocurrency-related data.
The separate Instagram incident, investigated by iVerify, involved a financial institution employee whose iPhone was reportedly infected after scrolling past a World Cup advertisement. Researchers linked the attack to a DarkSword variant, and the victim reportedly did not click the ad.
The distinction lies in how the malicious content reaches victims. DeadTag exploits abandoned third-party website dependencies, while the Instagram incident involved malicious advertising content.
Both cases illustrate how attackers can potentially compromise vulnerable devices through content that loads during ordinary browsing, without requiring the user to interact with a suspicious link.
When doing nothing becomes a security risk
Many cybersecurity recommendations focus on what users should and shouldn't do online.
When it comes to spyware, the usual advice is to avoid phishing links, a common way attackers trick victims into exposing themselves to malware.
However, threat actors keep adapting, and the attack techniques in these cases — malvertising and drive-by — themselves aren’t new.
What makes the techniques concerning is that, when chained together, they often defeat many cybersecurity recommendations and can compromise even the most careful users.
That exposes a limitation in advice that places too much responsibility on users to spot suspicious activity.
When malicious code loads automatically, the outcome can depend on device vulnerabilities and weaknesses in the systems delivering the content, not simply on whether someone makes a risky decision.
How iPhone users can reduce their risk
Although these attacks may not require victims to click malicious links, iPhone users can still take steps to reduce their exposure.
For starters, the malware checks a device's iOS version to determine which exploits might work. The documented campaigns primarily target older, vulnerable versions, although researchers have seen attempts to adapt the tools for iOS 26 and 27, with much of that newer code reportedly non-functional.
Modern browsers also have security features designed to block known malicious websites and make exploitation harder. Safari, for instance, uses Safe Browsing to block identified malicious domains, while built-in browser and operating system protections can stop some drive-by attacks before they succeed.
However, these measures cannot guarantee protection against every new exploit.
The most effective step is to keep iOS and browsers updated so known security vulnerabilities are patched. iPhone users at higher risk of targeted attacks can also consider Apple's Lockdown Mode, which restricts certain features that sophisticated exploits may rely on.
These precautions cannot eliminate every threat, but they can reduce the opportunities available to attackers. The reported incidents show why security depends on more than avoiding suspicious links: even familiar platforms and legitimate websites can become attack channels when vulnerabilities remain exploitable.
Other news: 1Password has introduced a feature that lets AI agents log in to online accounts without exposing users' passwords, although concerns remain about what agents can access and do after signing in.