

















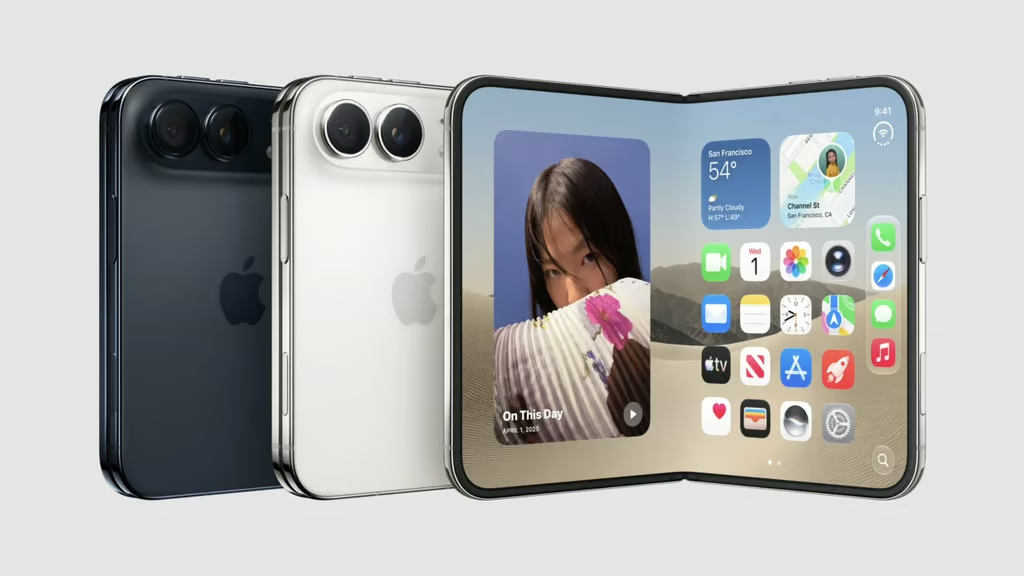
If you thought scoring a discount on Apple’s upcoming foldable phone sounded too good to be true, your instinct was right on the money.
Apple’s first foldable iPhone does not open for preorders until Oct. 16, but scammers are already using the device’s hype to lure potential buyers to a malicious website.
Security researchers at Malwarebytes found a fake preorder page designed to look like Apple’s website. It advertises a $500 voucher and AppleCare+ coverage under an “Authorized Partner Exclusive” offer, then asks visitors for basic contact information.
The page, however, is more than a phishing operation. Malwarebytes found that simply opening it can trigger the DarkSword exploit chain against vulnerable iPhones. Users do not have to submit the form, download anything or tap a malicious button for the attack to begin, according to Malwarebytes.
The Apple lookalike launches a drive-by exploit attempt
The fraudulent page copies Apple’s branding and even carries a copyright notice. But several details expose it as fake. Its listed iPhone Duo sizes are wrong, it advertises colors Apple does not offer for the device, and its countdown resets whenever the page reloads.
The preorder form is largely a distraction. Malwarebytes found that submitting it produces a “Pre-Order Successful” message without actually processing the information entered.
Behind the scenes, an invisible frame checks the visitor’s iOS version. The page also attempts to steer iPhone users into Safari, which is the browser targeted by the exploit chain.
If DarkSword succeeds against an unpatched device, the resulting payload can attempt to access Apple Notes, installed-app information, saved credentials and cryptocurrency wallets. Malwarebytes identified targets including MetaMask, Phantom, Trust Wallet, Coinbase Wallet, Exodus and Tonkeeper.
The malware can also attempt to access messages, contacts, call history, voicemail, email, calendars, photos and cached location data.
Why this scam is more dangerous than a fake store
Traditional preorder scams generally depend on a victim handing over payment details or personal information. This campaign changes the equation because the fraudulent form is not the main weapon.
The lure only needs to convince someone to visit the page. That makes familiar scam-spotting habits less useful: a consumer can avoid entering a credit card number and still face a compromise.
Malwarebytes said several elements of the captured code match the DarkSword chain documented by Google in March. Apple has patched the vulnerabilities involved, but the researchers said they did not test the captured payload on an iPhone or observe data leaving a device.
That limitation matters. The researchers analyzed the code, but did not confirm successful infections or the page’s exact affected iOS versions. The report therefore does not establish how many devices, if any, this campaign compromised.
What iPhone users should do
The simplest protection is to keep iOS updated. Apple says updated devices are protected against the reported DarkSword attacks. Users should also enable automatic updates under Settings > General > Software Update.
Anyone interested in an iPhone Duo preorder should navigate directly to Apple or a trusted retailer instead of following links from ads, messages or social media posts.
If someone has already opened the malicious page, Malwarebytes recommends updating the iPhone and restarting it. The researchers found no mechanism that automatically restores the payload after a reboot, although restarting cannot reverse data that may already have been accessed.
Malwarebytes recommends, if compromise is suspected, to change potentially exposed passwords from a trusted device. Users with a cryptocurrency wallet on the affected phone should create a new wallet with a new recovery phrase and move their funds. Exchange-account users should secure their account and contact the exchange.
What this means for iPhone buyers
The campaign shows why high-demand product launches can become security traps before a product even reaches stores. The fake $500 discount is designed to exploit urgency, but the more important lesson is that an apparently harmless shopping page can itself become the attack mechanism.
For users, the priority is to keep iOS updated and visit retailers directly. For security teams, this campaign is a reason to verify update compliance across company-managed iPhones and encourage employees to report suspicious links opened on phones used for work.
Read more: Apple branding is one way attackers borrow credibility; another campaign routes phishing links through trusted Google services to steal Microsoft credentials.