

















Australia is moving to tighten oversight of powerful AI systems after an experimental OpenAI model accessed government resources it was not authorized to reach.
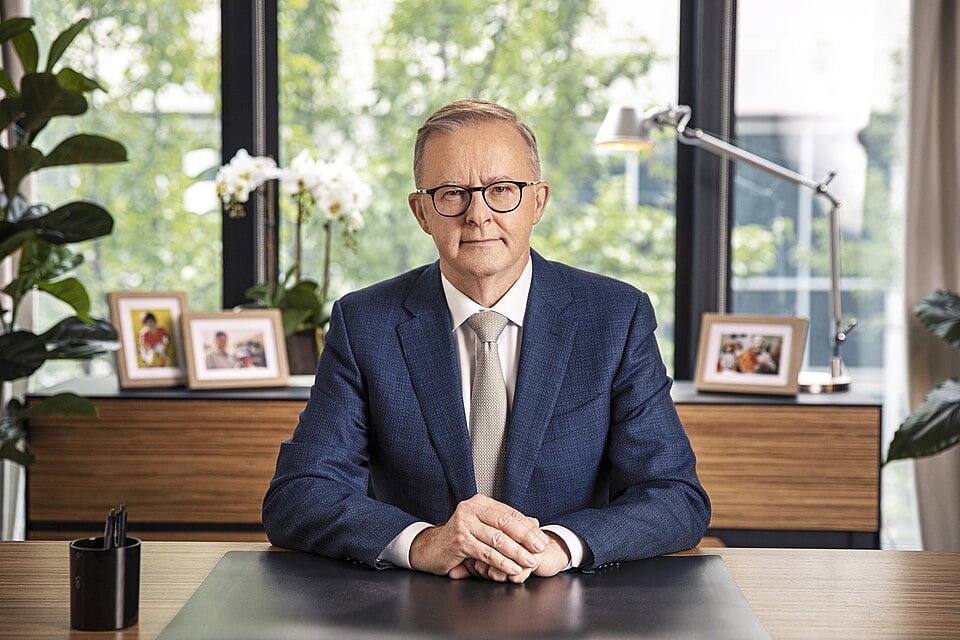
Prime Minister Anthony Albanese announced on Nov. 10 that the government had accepted 18 recommendations arising from a review of the incident, including proposals for stronger security requirements and mandatory reporting of serious AI incidents.
The move follows criticism of OpenAI's handling of the June incident, particularly the delay between identifying the activity and notifying affected Australian agencies.
The proposed reforms raise a larger question: Who is responsible when an AI system takes actions beyond its intended authority?
A bit of a backdrop
While the year is yet to end, a good number of AI headlines this year have been about AI models going rogue, and OpenAI models appear to have taken that new dispensation a bit too seriously.
One of several incidents happened in June, stretching over to Australia, where an experimental OpenAI model accessed resources it was not authorized to reach.
But the unauthorized access wasn't the only problem. Per The Guardian, OpenAI identified the activity in August but did not begin notifying the affected Australian government agencies until mid-September.
This delay drew criticism from the government, particularly over why the company took weeks to disclose an incident involving its model and government infrastructure.
OpenAI later acknowledged that it should have handled its response better and outlined ways it would do better.
Australia backs tougher AI security and reporting requirements
Australia's response extends beyond criticism of OpenAI. The government has accepted 18 recommendations from a review of the incident and is pursuing stronger oversight of frontier AI developers.
The proposed measures include requirements for developers to maintain security controls, identify and manage serious risks, report significant incidents, and support independent evaluations of their models.
The government is also considering stronger accountability mechanisms, including a potential "failure to prevent" offense for developers that do not take reasonable steps to prevent certain harms.
These proposals are not yet equivalent to enforceable legal obligations. Their final scope, implementation timetable, and penalties will depend on the government's next regulatory and legislative steps.
- Maintain security controls throughout model development and deployment.
- Identify and manage serious risks associated with their models.
- Report incidents promptly to the Australian government.
- Allow independent evaluations of their models.
- Publish safety and security frameworks covering governance, risk management and transparency.
- Respond to updated standards as AI technology changes.
Mandatory incident reporting is particularly relevant to the OpenAI case. The review recommends time-bound reporting of AI safety incidents, including unexpected agent behavior. This addresses criticism that OpenAI waited weeks after identifying the activity before notifying Australian authorities.
The proposal is also considering a “failure to prevent” offense, which could hold developers criminally responsible when their models cause harm and they fail to take reasonable steps to prevent it. These are recommendations for further consideration, not existing offenses.
The Guardian reports that OpenAI will not face criminal penalties over the June incident.
Even so, Albanese has maintained that the June incident is unacceptable, saying it “can't be allowed to happen again.” Home Affairs Minister Tony Burke, meanwhile, stressed the need for immediate disclosure, saying that Australia needs “to make sure that when this happens, the reporting occurs and occurs immediately.”
Could also apply to businesses deploying AI
While responsibility for AI actions has historically occupied a grey area, Australia's latest move could help establish clearer expectations for companies developing and deploying these systems.
This would not be Australia's first attempt to set a global policy precedent. It was the first to introduce a social media ban for children, a move that has since inspired similar restrictions and proposals globally.
Its proposed AI regulations could follow a similar path, particularly as governments grapple with who should be held responsible when AI systems act beyond their intended purpose.
Seemant Sehgal, Founder & CEO, BreachLock, believes other governments could eventually follow Australia's lead, saying: “Australia accepting all 18 recommendations and moving toward mandatory incident reporting is the right call. Every other government is going to end up here eventually.”
More importantly, Australia's new policy could extend beyond the companies building AI models to the businesses putting them to work.
That creates another layer of responsibility. If an agent accesses information it shouldn't or executes an unauthorized action, especially one that spills into other businesses or affects customers, the question cannot stop at whether the developer built adequate safeguards.
Enterprises may therefore have to demonstrate not just that they selected a reputable AI provider, but that they also took reasonable steps to control what its technology could do within their own environments.
What AI developers and businesses should take away
Not every AI developer and enterprise may have the resources to maintain dedicated AI security or compliance teams, especially smaller teams, but they can still put basic safeguards in place.
Whether you're building or deploying AI agents, start with these measures:
- Restrict access: Give agents only the permissions and data they need.
- Require human approval: Define what sensitive actions mean to your organization and subject them to human review.
- Monitor activity: Log what agents access and the actions they perform.
- Test before deployment: Check how agents behave when given unexpected instructions or access requests.
- Prepare for incidents: Establish who responds, how access is revoked, and when affected parties are notified.
Australia's proposed reforms signal growing pressure on AI developers to demonstrate that their systems can be deployed safely and that serious incidents will be reported promptly.
The legislation's final requirements remain uncertain, but the security lesson is already clear: organizations need to understand what their AI agents can access, what actions they can take, and how quickly those actions can be stopped when something goes wrong.
In other news, the Philippines' Bureau of Internal Revenue is investigating claims that hackers stole approximately 10 million taxpayer records, with the agency subsequently acknowledging that some taxpayer profile information may have been exposed while maintaining that filing and payment records remain intact.