

















SolarWinds lacks the full security suite presence of some competitors, but is well-integrated across a variety of bonus IT operation capabilities such as threat intelligence platform capabilities, privileged access management, USB security, and botnet detection.
These additional capabilities make the SolarWinds SEM a good fit for SMEs who may lack their own internal security teams — and particularly those looking for integrated IT management capabilities too. The company targets tightly resourced, budget-conscious security teams, in organizations with up to 10,000 employees, and often cites compliance as a driver.
For a comparison with other products, see:
Company Description
Since 1999, SolarWinds has been providing management and monitoring software for security, networks, servers, applications, storage, databases, virtualization and the cloud. It trades on the NYSE under the symbol SWI.
Product Description
SolarWinds Security Event Manager (SEM) is composed of several key elements:
- Manager for central management, log and event management, and storage
- Console and user interface
- SEM Agents for real-time event collection from endpoints, encryption and compression of data
Network traffic, application, and virtualized platform monitoring can be tied into SEM through the SolarWinds Virtualization Manager, the Network Performance Monitor, and the Server & Application Monitor. SolarWinds Security Event Manager (SEM) 2022.4 supports log forwarding to other applications, as well as SolarWinds SEM deployments on Azure.
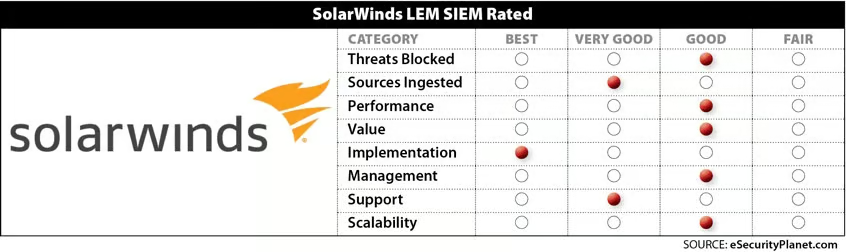
SolarWinds SIEM Features Rated
Threats Blocked: Good. SEM ships with hundreds of predefined correlation rules, including authentication, change management, network attacks, and more. SolarWinds SEM also integrates with online threat feeds and can notify and respond to inbound/outbound traffic and authentication attempts with known bad IP addresses for threats such as ransomware, malware, spam, phishing, and more.
Breadth of Sources: Very good. SolarWinds SEM includes seven hundred log parsers. There is a process in place for users to request new connectors or updates to existing connectors. SolarWinds SEM supports a variety of event sources, including nonevent data sources that can be integrated into its analytics and correlation rules.
Throughput: Good. While SolarWinds SEM can support several thousand nodes, it rarely sees users exceed 2,000 EPS. Most customers store between 2 to 8 TB of data, but users have the option of scaling beyond 8 TB.
Value: Good. SolarWinds provides good value in overall cost and time to implement.
Implementation: Best. Users praise the product’s ease of implementation. SolarWinds SEM is deployed as a self-contained virtual appliance, which includes the SolarWinds SEM database, correlation engine, and all other components required. It can be deployed typically within minutes. Analysts have complimented SolarWinds on its simple architecture, easy licensing, and robust out-of-the-box content and features.
Management: Good. Ease of use is an area of frequent praise, but there are some limitations in its ability to integrate with third-party advanced threat detection, threat intelligence feeds and User Behavior Analytics (UBA) tools.
Support: Very good. SolarWinds has been recognized for its technical support and customer success programs globally. An assisted onboarding program provides access to implementation experts who work with users to understand their goals, assist in installing and configuring the product, and help optimize their environments based on business needs.
Scalability: Good. SEM’s architecture scales horizontally to support thousands of nodes, but may not scale as well vertically.
Intelligence
SolarWinds Security Event Manager customers leverage pre-defined correlation rules targeted at user and system change monitoring. These rules include direct change auditing (user permission, metadata, group memberships, etc.) and system change auditing (policies, files, etc.). Thresholds for behavior can be applied to differentiate normal from abnormal behavior.
Delivery
Virtual appliance for VMware and Hyper-V platforms, plus a deployment option for Azure.
Agents
The SolarWinds SIEM platform employs agents.
Pricing
SolarWinds SEM does not explicitly list pricing on their website, however, they allow potential customers to browse products and generate a quote. Subscription licenses for one to five years start at $2,877; perpetual licenses start at $5,607 for the software and one year of support with options to purchase yearly ongoing maintenance and support.
The SolarWinds license is based upon the number of nodes (server, network device, desktop, laptop, etc.) sending log and event information and tiered pricing is available for bulk-use discounts or multiple-software license discounts. License costs include log management, agents, connectors, file integrity monitoring, USB Defender, external threat feeds, and all SIEM components.
A Workstation Edition license enables SolarWinds SEM customers to extend deployments to Windows workstations. Consulting and professional services are typically not required.
For more analysis of SolarWinds Security Event Manager, see SolarWinds vs Splunk: Top SIEM Solutions Compared.
This article was originally written by Drew Robb on November 5, 2018, and updated by Chad Kime on February 7, 2023.