

















Cybersecurity experts are warning website owners after hackers began actively exploiting two critical vulnerabilities in Craft CMS, a content management system, leaving hundreds of servers compromised.
The flaws — CVE-2024-58136 and CVE-2025-32432 — were discovered by Orange Cyberdefense’s SensePost team during a forensic investigation in mid-February. Their research revealed that attackers are using these bugs to breach servers, upload malicious files, and gain unauthorized access.
In a blog post, Orange Cyberdefense explained that on Feb. 14, their team was asked to investigate a hacked server running CraftCMS version 4.12.8. Their analysis uncovered the two vulnerabilities and signs of active exploitation.
“On the 10th of February, a threat actor compromised a web server using CVE-2025-32432, which affects all Craft CMS versions from 3.x to 5.x,” said the April report. “Between the 10th and the 11th of February, the threat actor improved their scripts by testing the download of filemanager.php to the web server multiple times with a python script. The file filemanager.php was renamed to autoload_classmap.php on the 12th of February and was first used on the 14th of February.”
How the attack works
The more serious of the two flaws, CVE-2025-32432, allows remote code execution (RCE) through Craft CMS’s image transformation feature. According to SensePost’s report, the vulnerability lets an unauthenticated attacker send specially crafted POST requests to manipulate the server.
Security researcher Nicolas Bourras explained in the report, “CVE-2025-32432 relies on the fact that an unauthenticated user could send a POST request to the endpoint responsible for the image transformation and the data within the POST would be interpreted by the server.”
In simpler terms, hackers would repeatedly send requests until they found a valid “asset ID,” a number that identifies images and files in the CMS. Once a valid ID was found, they would send malicious data that the server would unknowingly execute, allowing hackers to upload a PHP file manager onto the server.
Hundreds of Servers at Risk
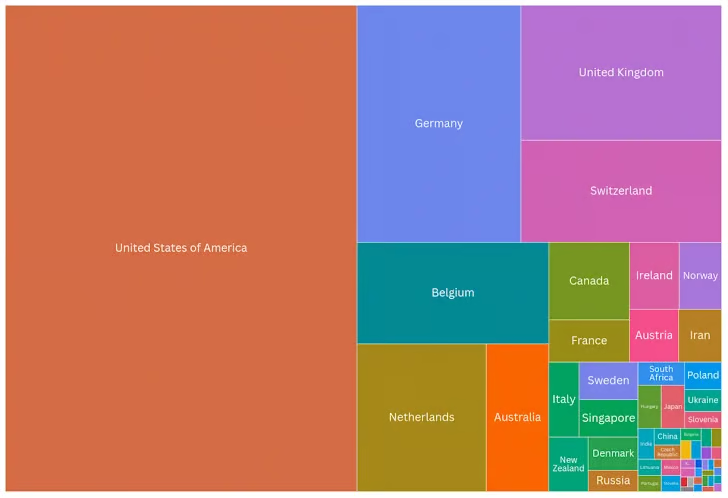
Orange says about 13,000 Craft CMS instances remain vulnerable, and roughly 300 servers have likely been compromised so far.
Craft CMS confirmed it became aware of the vulnerability on April 7, 2025. Three days later, it quickly issued patched versions — 3.9.15, 4.14.15, and 5.6.17 — urging users to update immediately.
In an official advisory, Craft CMS stated, “If you check your firewall logs or web server logs and find suspicious POST requests to the actions/assets/generate-transform Craft controller endpoint, specifically with the string __class in the body, then your site has at least been scanned for this vulnerability”. They stressed that being scanned doesn’t necessarily mean the site was hacked.
Craft CMS also provided detailed mitigation advice, urging users to refresh their security keys, rotate database credentials, and force password resets for all users if they suspect a breach.
Chaining vulnerabilities
The attacks have been particularly devastating because hackers are chaining both CVEs together. CVE-2024-58136, rated 9.0 out of 10 on the CVSS severity scale, is a flaw in the Yii PHP framework used by Craft CMS. It allows unauthorized access to restricted resources, adding another layer of danger to already exposed servers.
Lessons and warnings
Experts emphasize that any site still running outdated versions of Craft CMS is highly vulnerable. They also warn that similar tactics could be used against other CMS platforms if administrators fail to patch critical flaws quickly.
Meanwhile, Craft CMS reminded users, “Regardless of where you are hosted, we always recommend keeping your sites up-to-date so that they include the latest security fixes.” With active attacks ongoing, organizations are being urged to patch their systems, check server logs for suspicious activity, and tighten their security controls immediately.